

Recent cybersecurity incidents involving 6 healthcare entities did not disrupt patient care: MOH
There is no evidence so far that patient safety and care have been compromised, the Ministry of Health said.
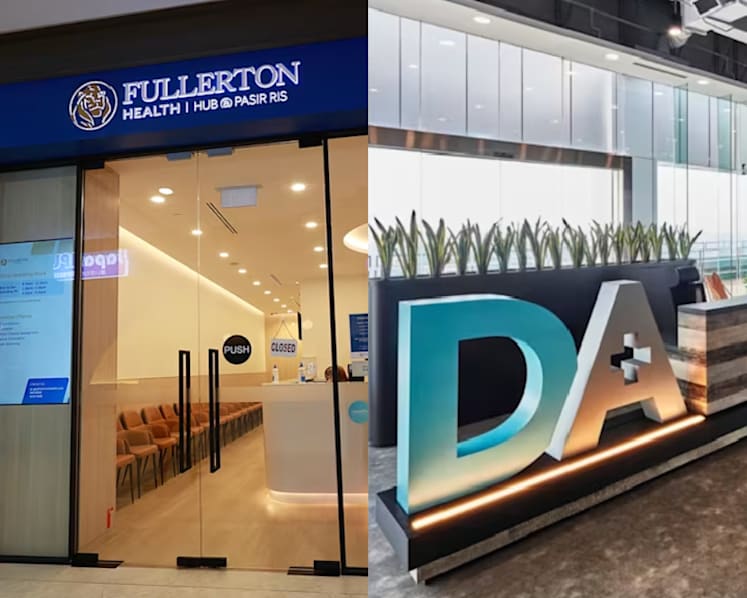
A view of Fullerton Health Hub Pasir Ris and a sign showing Doctor Anywhere's logo. (Photos: CNA, Facebook)

This audio is generated by an AI tool.

SINGAPORE: The Ministry of Health (MOH) is taking the recent spate of cybersecurity incidents across the healthcare sector very seriously, it said on Thursday (Nov 12).
The breaches have not disrupted patient care operations, and there is no evidence so far to suggest that patient safety and care have been compromised, MOH said in a statement.
“To our knowledge, there had not been unauthorised access of patient health records in these breaches,” the ministry added.
Nevertheless, MOH is following up with the affected entities - including the Agency for Integrated Care (AIC), Alliance Medinet, Doctor Anywhere Group, Fullerton Health Group, Minmed Group and Dementia Singapore - to assess the full implications of the recent incidents.
The affected entities are working closely with cybersecurity consultants and the relevant authorities, including the Cyber Security Agency of Singapore (CSA) and the Personal Data Protection Commission (PDPC) to follow up on the breaches.
Recent healthcare data breaches
Oct 24: Alliance Medinet
Personal data of about 110,000 members was compromised after unauthorised access to its membership database, including names, identification numbers and contact details. Bank details of seven members and one member’s medical diagnosis might also have been affected. Nearly 4,400 customers of HSBC Life, Income Insurance and Singlife were affected or potentially affected.
Nov 6: Doctor Anywhere
Users’ personal data was leaked in a cyber incident involving an unknown third party. Doctor Anywhere, which became aware of the breach on Oct 29, did not disclose how many users or what data were affected, but said clinical records were not compromised.
Nov 9: Fullerton Health
A server supporting its Migrant Worker Primary Care Plan programme was accessed without authorisation. Fullerton Health did not disclose how many workers were affected, but said names, FIN numbers, dates of birth and contact details may have been exposed, while health, medical and financial information were not affected.
Nov 11: Dementia Singapore’s CARA SG app
Some CARA SG members’ personal data may have been compromised after a cyber incident that saw unauthorised app notifications being sent on Nov 1. Names, email addresses, phone numbers and membership IDs may have been affected, but no NRIC numbers were compromised.
Nov 11: Minmed Group
A standalone system supporting Minmed’s teleconsultation and health screening services was hit by a “malicious cybersecurity incident”. The group did not disclose the number of people or types of personal data affected, but said clinical records were not compromised.
Nov 12: Agency for Integrated Care (AIC)
An unauthorised third party accessed AIC’s Advance Care Planning IT system, potentially compromising the personal data of up to 4,064 staff from public healthcare institutions and community care providers. Names, contact details and NRIC numbers may have been affected, but no indications were found that medical records or patient data had been compromised.
MOH has asked Synapxe and the public healthcare institutions to stay vigilant and increase monitoring for potential cyber threats across public healthcare IT systems.
Private healthcare providers were also advised to review and strengthen their cybersecurity measures to protect their systems and health information.
“These incidents underscore the importance of being vigilant and despite the best of efforts, every IT system is vulnerable to the most determined attack.
“With the advancement of technology, especially AI, vulnerabilities will be easily exposed and cyberattacks more frequent, rapid and formidable.
“MOH reminds all licensed healthcare institutions and Healthcare Information Management System providers to remain vigilant, strengthen their cybersecurity posture, and ensure the security and integrity of their IT assets, systems, and patient data.”
Earlier on Thursday, AIC said it had detected a cybersecurity incident on Nov 10 in which the personal data of up to 4,064 employees of public healthcare institutions and community care providers may have been accessed.
Healthcare and healthcare-related organisations Minmed, Fullerton Health, Doctor Anywhere and Dementia Singapore have also disclosed cybersecurity incidents over the past week.
On Nov 6, Doctor Anywhere said users’ personal data was leaked in a “malicious cyber incident”. Cybersecurity consultant Ensign InfoSecurity said clinical records were not affected.
Three days later, Fullerton Health said its Migrant Worker Primary Care Plan programme was affected by a cybersecurity incident involving unauthorised access.
Dementia Singapore and Minmed both disclosed cybersecurity incidents involving their systems on Nov 11.
Preliminary investigations found that migrant workers’ full names, FIN numbers, dates of birth, mobile numbers, email addresses and residential addresses may have been affected.