

Minmed reports 'malicious cybersecurity incident' involving teleconsult, health screening system
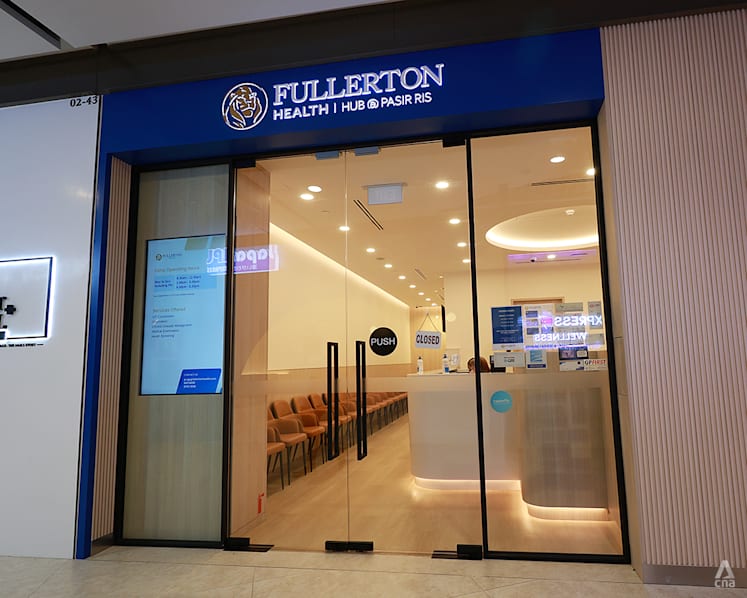
This is the third cybersecurity incident reported by a healthcare provider in the past week, after Fullerton Health and Doctor Anywhere disclosed cyberattacks.
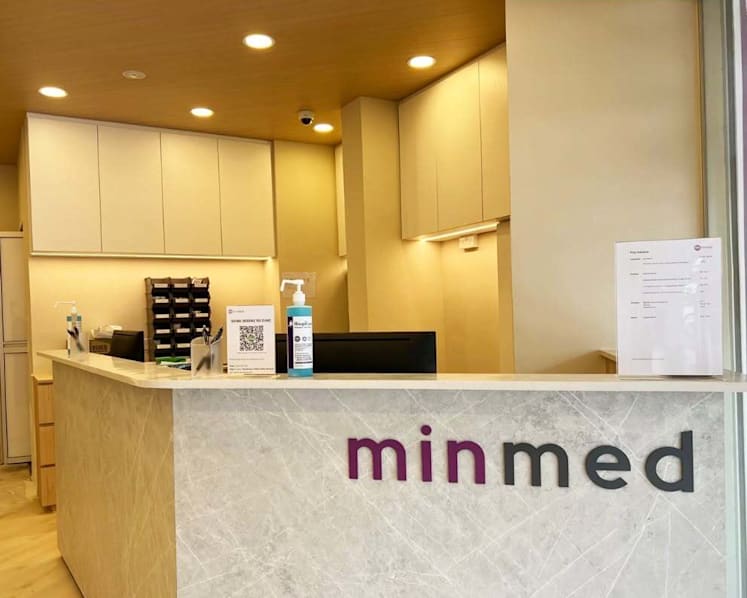
A Minmed clinic in Singapore. (File photo: Facebook/Minmed Group)

This audio is generated by an AI tool.

SINGAPORE: A system supporting Minmed Group's teleconsultation and health screening services was affected by a "malicious cybersecurity incident", the healthcare provider said on Wednesday (Nov 11).
"Based on our investigations to date, the incident appears to be limited to a specific standalone system supporting our teleconsultation and health screening business."
It added that clinical records were not affected by this incident.
Minmed also runs general practitioner, dental and paediatric clinics, and provides healthcare and wellness services.
"Upon discovery of the malicious threat, we acted immediately to contain the incident," the group said, adding that it engaged Ensign InfoSecurity to support a formal investigation and strengthen its systems.
Minmed said that it had taken steps to address the identified vulnerabilities and would continue working with Ensign InfoSecurity to monitor and strengthen its cybersecurity measures.
As of Nov 5, Ensign InfoSecurity had independently validated the security fixes deployed and confirmed that the identified vulnerabilities in Minmed's system had been secured.
Minmed had reported the incident to the Personal Data Protection Commission (PDPC) and made a police report.
"We are cooperating fully with all relevant authorities to support their investigations," it added.
All of its healthcare services and clinics remain operational.
"We recognise the trust placed in us, particularly when it comes to the handling of personal and health-related information," the healthcare group said.
"Protecting that trust remains our priority, and we sincerely apologise for any concern this incident may cause."
It also said that it could not provide more details while investigations were ongoing.
This is the third cybersecurity incident reported by a healthcare provider in the past week, after Fullerton Health and Doctor Anywhere disclosed cyberattacks.
Around 110,000 insurance customers' data was compromised in an Alliance Medinet data breach in October.
On Nov 6, telco M1 and telehealth provider Doctor Anywhere reported data breaches.
The M1 data breach exposed customers' personal information, including names, identity card numbers, dates of birth, mobile numbers, email addresses and residential addresses.
Doctor Anywhere also reported a leak of users' personal data, although cybersecurity and forensic specialist Ensign InfoSecurity said then that clinical records were not affected.
Separately, Singapore Airlines announced on Nov 3 that a data breach compromised around 46,000 booking records.
On Tuesday, SPH Media said that five of its systems were hit by cyberattacks, while food solutions provider SATS said that Tappee, a school meal ordering application, had been affected by a cyber incident.
SATS added that the Tappee incident involved "malicious access by an unauthorised external party".
Four schools in Singapore now use the app. Based on investigations so far, the compromised data includes student names, email addresses, financial assistance statuses, student concession card numbers and certain parent and guardian email addresses.
In response to a previous query by CNA, SATS declined to name the schools "to protect the privacy and interests of affected students and families".